Category : Reverse Engineering
Description :
Hello players, this is serious you have to hack !! today you are gonna learn a new command !!! the hint is given in the name of the BINARY. First of all ? what is a binary ? what is an executable ??tutorial ?there is magic called DECOMPILATION ! you can do it with many tools like GHIDRA or IDA also this website works wellDogbolt
GOOD LUCK !! (you will need it , this challenge is very hard !!!)
𝐀𝐮𝐭𝐡𝐨𝐫 : 𝐁𝐥𝐚𝐜𝐤𝐤𝐚𝐝𝐞𝐫
Files Given : a binary 'stringz'
Solution
The first we usually use while reverse engineering is the file command
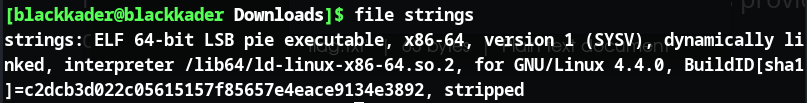
We can see that it's an executable which is built for 64-bit and compiled for the x86-64 (AMD64) architecture and for Linux kernel version 4.4.0 or newer.
You have to learn more about the file command !!!!!!!
Running the file won't give us anything useful :/
So let's try to use this website Dogbolt which was provided in the description, we get this result :
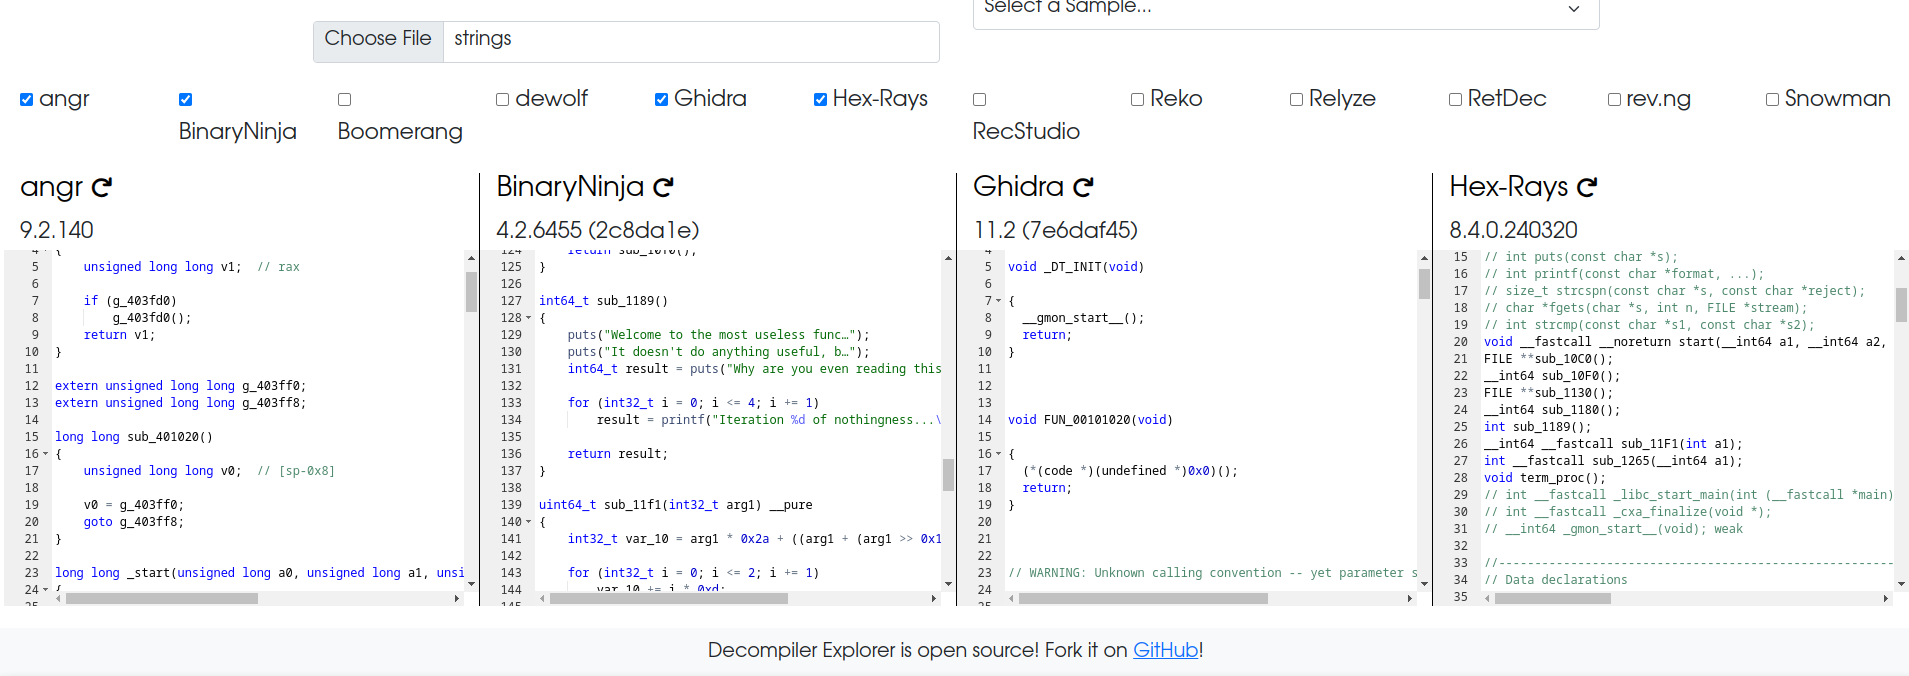 Let's choose any one of those and try to search for the flag format FL1TZ
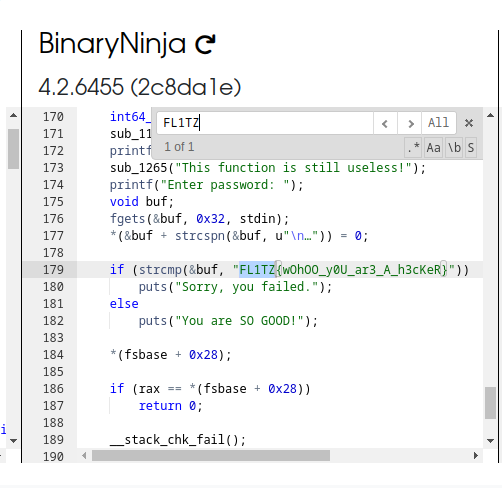
And we find our flag :
FL1TZ{wOhOO_y0U_ar3_A_h3cKeR}
There is another way to solve this challenge ! And it is the intended way :
As it says in the description (the hint is given in the name of the BINARY)
What is the name of the binary ? "strings"
A beginner Linux user will know what we exactly want here , which is the strings command, let's try to use it on our binary
If you had typed the name of the binary twice (with a space in between), you would have gotten the flag xD
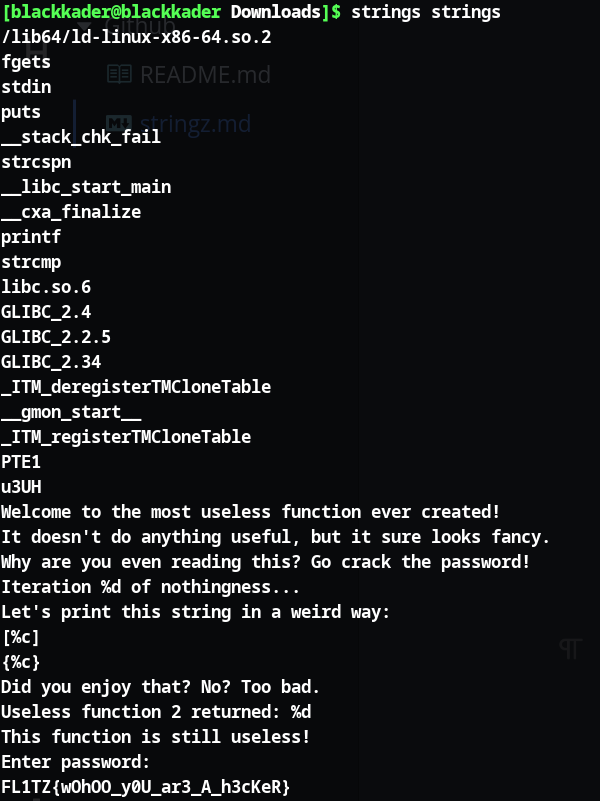
MUST KNOW : file and strings are the number one step we always do in each challenge , they are information gatherers and our bestfriends !!